Has GrapheneOS Been Cracked? What Recent Police Cases Reveal About Pixel and GrapheneOS Security


No confirmed case to date shows law enforcement remotely accessing a phone running genuine, up-to-date GrapheneOS. Every confirmed case we are aware of involves a seized device that investigators had physically in their hands, and in the most recent Dutch case the phones ran a reseller's own modified system with remote management built in.
Reports that police have 'cracked' GrapheneOS have spread through privacy forums, the press and criminal defence circles across Europe, most recently in Germany and the Netherlands. Two cases drive the debate. In Hamburg, Germany's Federal Criminal Police Office (BKA) extracted data from a seized Google Pixel 8a documented as running GrapheneOS, a year after a first attempt had failed. In the Netherlands, police raided the homes of customers of a Pixel reseller from Ridderkerk in late October 2026. Both cases show under which conditions a phone becomes readable for investigators.
What Is GrapheneOS?
GrapheneOS is a free, open-source mobile operating system based on the Android Open Source Project (AOSP). It is developed by the GrapheneOS Foundation, a Canadian non-profit organisation, and has around 400,000 users worldwide (CTV News). Google services are not preinstalled; users who need them can run Google Play in a sandbox like any ordinary app.
GrapheneOS officially supports only Google Pixel phones, currently from the Pixel 6 to the Pixel 10 series. The reason is hardware: Pixels allow the bootloader to be re-locked with a third-party operating system, so verified boot stays intact; they check PIN attempts in a dedicated secure element; and they receive security updates for many years. In March 2026 the project announced a partnership with Motorola, whose first GrapheneOS devices are expected in 2027 (It's FOSS).
Three protections matter most against forensic extraction (GrapheneOS features):
an automatic reboot of a locked phone, by default after 18 hours (configurable from 10 minutes to 72 hours), which returns the data to the fully encrypted 'Before First Unlock' (BFU) state,
blocking of new USB connections while the phone is locked, which closes the port that forensic tools typically use,
a hardened memory allocator and, from the Pixel 8 onwards, hardware memory tagging (MTE), which make security flaws harder to exploit.
This level of protection has drawn police attention across Europe. Police in Catalonia have publicly associated Pixel phones running GrapheneOS with drug trafficking (Notebookcheck). After Le Parisien portrayed GrapheneOS as a tool of drug traffickers in November 2025, the project moved all of its active servers out of France (Proton). GrapheneOS is nonetheless a lawful tool, used by journalists, activists, lawyers and businesses that need to protect confidential information.
Can Cellebrite Unlock GrapheneOS?
Cellebrite, the Israeli vendor whose extraction tools are used by police forces worldwide, does not publish its capabilities. Internal support matrices have nonetheless leaked several times since April 2024, most recently in October 2025, when someone joined a Microsoft Teams briefing for prospective customers and posted screenshots. According to these documents, Cellebrite can extract data from Pixel 6 to Pixel 9 phones running Google's stock Android to a large extent. Locked Pixels running up-to-date GrapheneOS are listed as inaccessible; the matrix shows access only for GrapheneOS versions with a patch level older than late 2022 (Android Authority, reporting on 404 Media).
A leaked table captures a single moment, and forensic vendors work continuously on new methods. The documents still show a clear gap between stock Android and GrapheneOS on the same hardware. Reports from police practice point the same way: in Toronto, investigators were reportedly unable to unlock a GrapheneOS phone seized in connection with raids in June 2026 (Borncity, citing The Globe and Mail).
Remote Hacking or Extraction From a Seized Phone?
Any assessment of GrapheneOS security has to separate two scenarios.
In a remote attack, authorities access a phone that remains with its user and read stored data or live communications. This is done with spyware or through a provider's infrastructure, as in the EncroChat and ANOM operations. An attack on infrastructure can reach every user of a system at once without anyone noticing. In many European jurisdictions it requires a specific statutory hacking power, for example section 100b of the German Code of Criminal Procedure (StPO) or Articles 126nba and 126uba of the Dutch Code of Criminal Procedure (Sv), and it engages the right to private life under Article 8 ECHR.
In forensic extraction, the phone has been seized and sits in an evidence store. Examiners then try to defeat the lock screen, for instance through vulnerabilities in the USB interface, by automated guessing of the PIN, or with a PIN obtained in some other way. Success depends on the state of the device at the moment of seizure: its security patch level, whether it had been unlocked since its last reboot, and the strength of the PIN or passphrase.
Every confirmed case involving GrapheneOS devices that we know of falls into the second category. A seized phone receives no further updates and stays frozen at the patch level of the day it was taken. A vulnerability discovered months later, and long since fixed for everyone else, can still be used against it. A successful extraction from an old exhibit therefore says little about the security of a current, updated phone.
The Hamburg Case: German Police Extract Data From a GrapheneOS Pixel 8a
In proceedings before the Regional Court of Hamburg (Landgericht Hamburg), we have reviewed a note by the Hamburg State Criminal Police Office (LKA) and a forensic report by the BKA. According to the note, a seized Pixel 8a running GrapheneOS was handed to the LKA's specialist unit for extraction in June 2025. In July 2025, extraction was not possible.
A year later it was. The BKA's forensic science institute secured the internal storage, and the BKA's IT forensics unit processed the data with Cellebrite Inseyets Physical Analyzer, making it available for analysis on 2 July 2026. This establishes that German authorities obtained the data of at least one Pixel documented as a GrapheneOS device.
The documents do not say how. In particular, they leave open
how the lock was overcome (exploiting a vulnerability, guessing the PIN, or a PIN known from another source),
which patch level the phone had when seized and whether it was in the BFU or 'After First Unlock' (AFU) state,
whether it actually ran official GrapheneOS; the police note names the system without explaining how this was established.
The timeline suggests that the method was not available to the authorities in summer 2025. Because the exhibit remained at its 2025 patch level, the result allows only limited conclusions about current, patched devices.
For the defence, the case sets out a clear checklist. The method, the tools and versions used, the extraction logs and the hash values belong in the case file. Without them, neither the integrity of the data nor the lawfulness of the process can be tested. It is the same 'black box' problem that has shaped EncroChat and SkyECC proceedings for years: the authorities withhold the technique and expect the defence to accept the result.
The Ridderkerk Case: A Home-Made Fork, Remote Management and Compromised Signing Keys
On 26 and 27 October 2026, Dutch police searched homes across the Netherlands, including in Eindhoven, Zaandam, Hilversum and Dordrecht, with a focus on the Rotterdam area. According to the Algemeen Dagblad, officers were specifically looking for Google Pixel phones. Those searched were customers of the same reseller from Ridderkerk, and according to their lawyers several of them were told during the searches that they were not suspects.
The 42-year-old reseller was arrested on 26 October, which the Rotterdam Public Prosecution Service (Openbaar Ministerie) has confirmed. He is suspected of money laundering and participation in a criminal organisation and remains in pre-trial detention (Crimesite). Police and prosecutors have declined to comment on the searches or the scope of the investigation.
According to our information, the reseller did not distribute official GrapheneOS. Using AI tools, he had built his own fork and added mobile device management (MDM) for remote administration. The result was a separate operating system that lacked, among other things, the security updates of the original project.
His signing keys for that system were probably compromised. Anyone holding those keys can build an update that the phones accept as genuine. Such an update was apparently installed on seized phones via ADB (Android Debug Bridge), an interface that requires a USB cable connection, and probably removed the screen lock. The phones could then be examined forensically. On our information, the authorities again needed the phone in their hands. On official GrapheneOS, the same approach would require the project's own signing keys.
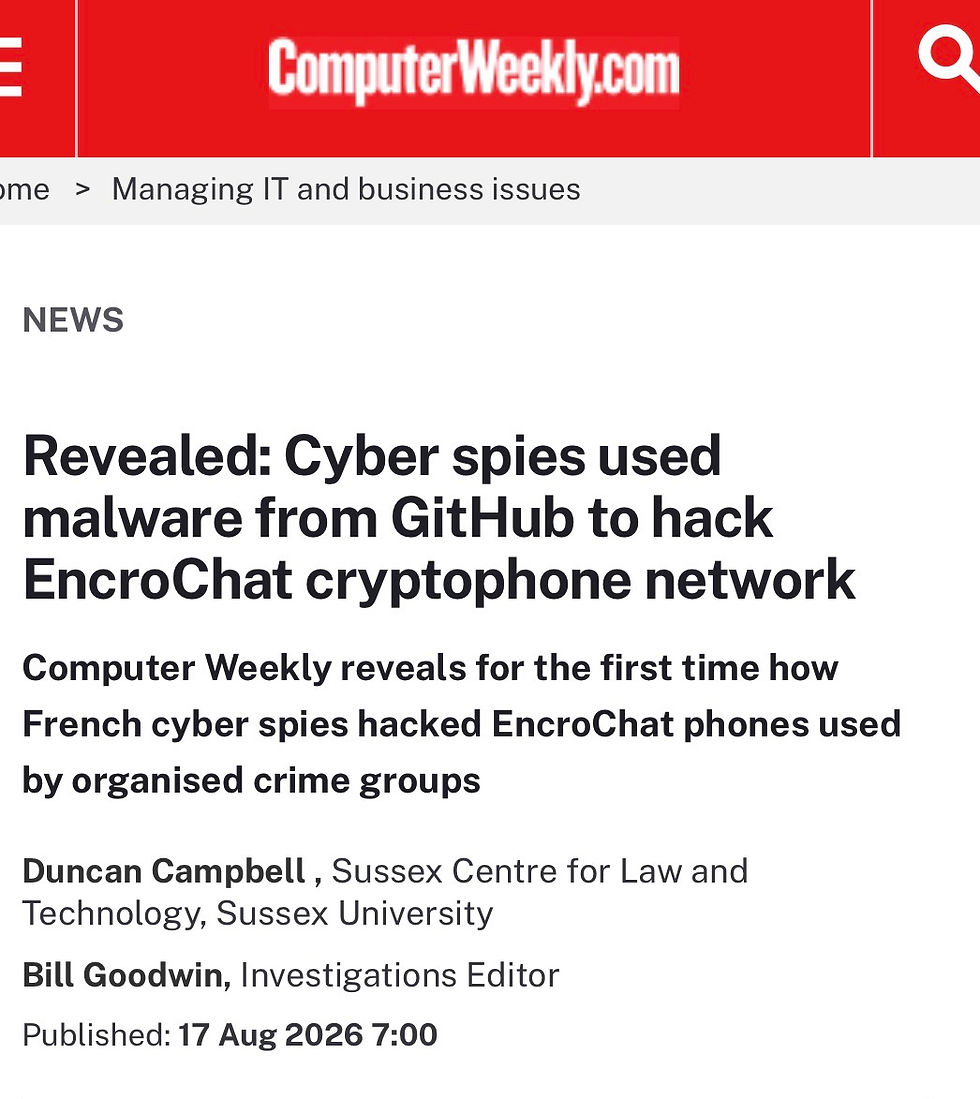
The parallel with EncroChat lies in the update channel. In 2020, French investigators used the provider's servers to push a manipulated update to EncroChat handsets. Whoever controls the update mechanism decides what software runs on the devices.
Phones sold by the reseller have continued to receive updates since his arrest. Who has been distributing them, and what they contain, is unknown. Every phone from this source should therefore be treated as compromised. The case tells us nothing about the security of GrapheneOS itself: the attack targeted a proprietary derivative through its own infrastructure.
Is a Google Pixel Secure Without GrapheneOS?
A Google Pixel is an ordinary phone sold on the high street. As the Cellebrite documents show, Google's stock Android does not reliably protect a locked Pixel against commercial forensic tools. There are also many alternative operating systems and commercial variants for Pixels. Some require a permanently unlocked bootloader, ship security patches late or switch off protective features, leaving the phone less secure than the original.
In our assessment, GrapheneOS is probably the most secure option currently available for Pixel phones. Its source code is public and reviewed by a large community, and the project releases security updates regularly. That protection depends on conditions: a supported device still within its update period, updates installed promptly, and a strong PIN or passphrase. For new purchases the project recommends a Pixel 8 or later. It has advised against buying the Pixel 11, released in August 2026, in the expectation of GrapheneOS support, because it remains unclear whether and when a release will follow (heise online).
Why You Should Avoid 'GrapheneOS Phones' Sold on Subscription
GrapheneOS is free. It is installed through the official web installer at grapheneos.org, and the project recommends buying a Pixel from a regular retailer and installing the system yourself.
Phones marketed as 'GrapheneOS phones' on a monthly subscription often run something else: a fork with remote management, the vendor's own update server and the vendor's own signing keys. Through that infrastructure the vendor can push software to the phone at any time, including malware. Android's own device management framework can also be configured so that an administrator is able to reset the screen lock. If the keys are lost or seized, or the vendor cooperates with the authorities, the same route is open to others. ANOM showed how far this can go: an FBI-controlled platform whose handsets were sold through distributors to criminal networks worldwide.
GrapheneOS itself warned about this risk in August 2026, after the Netherlands Forensic Institute (NFI) had unlocked a Pixel in a Dutch murder case without naming the operating system. According to the project, commercial forks often switch off precisely the USB protection and the auto-reboot timer, and some vendors charge a monthly fee and install software that lets them control the phones remotely (Cybernews).
Anyone who has received a phone with a preinstalled system can check whether it really runs official GrapheneOS. The project explains how in its installation guide.
What This Means for Users and for the Defence
The reports of a 'cracked' GrapheneOS do not hold up on closer examination. In Hamburg, the BKA extracted data from a seized phone a year after a failed first attempt, using a method it has not disclosed. In Ridderkerk, the authorities exploited a proprietary derivative with remote management through its own update channel. Neither case shows remote access to a phone running current, official GrapheneOS.
In any case involving data extracted from a Pixel, defence lawyers should establish
which operating system actually ran on the phone and how this was determined,
its patch level and lock state at the time of seizure,
which method and which tools were used to defeat the lock,
whether the authorities installed software on the phone and thereby altered the evidence,
what legal basis covered any intervention through a third party's update channel.
Installing an update on a seized phone alters the exhibit itself. Whether ordinary search and seizure powers cover such an intervention is an open question in many jurisdictions; at the very least, data integrity and full documentation of every step become central issues. If manipulated updates reached phones still in their users' hands, that would amount to covert remote hacking, which needs its own statutory basis. The Dutch hacking powers, for example, apply only to a device in use by a suspect, and several of the people searched in October were told they were not suspects.
As in the EncroChat and SkyECC cases, the fairness of the proceedings under Article 6 ECHR ultimately depends on whether the defence can test the method used.
Frequently Asked Questions About GrapheneOS Security
Can police remotely hack a phone running GrapheneOS?
There is no public evidence of remote access to a phone running current, official GrapheneOS. All confirmed cases we know of involve phones that police had seized.
Can Cellebrite unlock GrapheneOS?
Leaked Cellebrite documents up to October 2025 list locked Pixels with up-to-date GrapheneOS as inaccessible. Access was shown only for GrapheneOS versions with a patch level older than late 2022.
Did German police crack GrapheneOS?
In a case before the Regional Court of Hamburg, the BKA made the data of a seized Pixel 8a documented as running GrapheneOS available for analysis on 2 July 2026, a year after extraction had failed. The method has not been disclosed, and the phone's patch level and operating system build are unknown.
Were the Pixel phones seized in the Netherlands running GrapheneOS?
According to our information, they ran a reseller's own fork with remote management. Investigators were probably able to open seized devices because the reseller's signing keys were compromised.
Are GrapheneOS phones sold on subscription safe?
Subscription phones often run modified forks with remote management, through which the vendor can install software on the device. Official GrapheneOS is free and can be installed by the user on a Pixel bought from a regular retailer.
Is a Google Pixel secure without GrapheneOS?
With Google's stock Android, locked Pixel 6 to Pixel 9 phones were largely accessible to Cellebrite according to the leaked documents. GrapheneOS adds protections such as an auto-reboot timer and USB blocking that target exactly these extraction methods.
How can I check whether my phone runs genuine GrapheneOS?
Follow the verification steps in the official GrapheneOS installation guide.